Lucid agent models: build a bounded workflow before an autonomous system
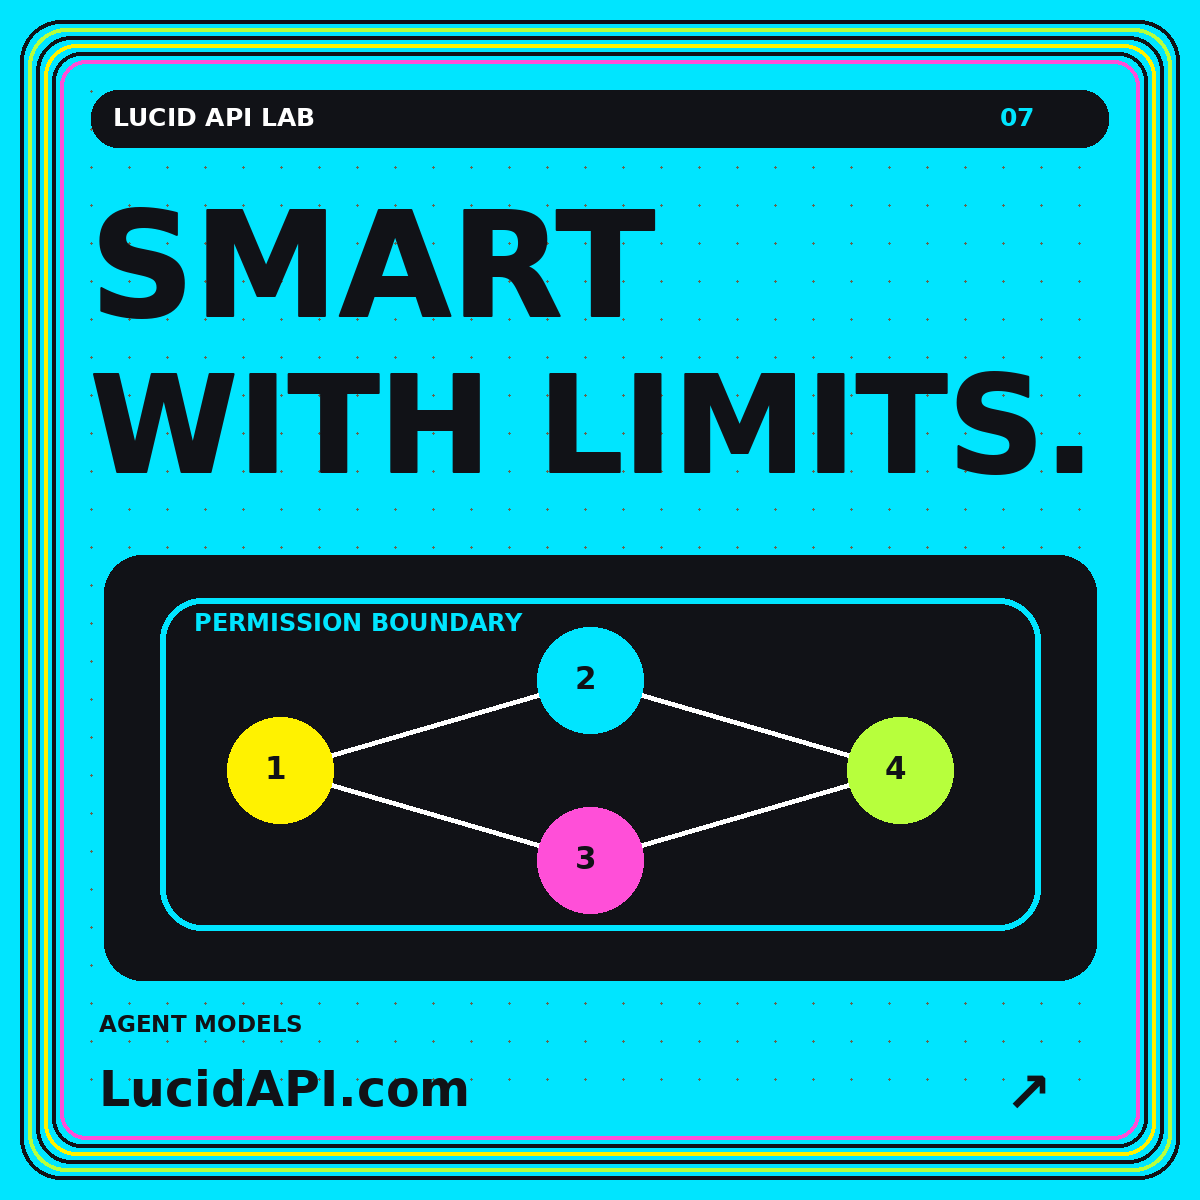
Choose between a fixed workflow and model-directed actions, then define tool permissions, approval points, stop rules, and recoverable state.
LUCID API LAB / TOPIC THREAD
Follow every copy of the information.
Privacy-related engineering begins with knowing what is collected, where it moves, and who can access it. These guides follow original entries into generated summaries, exports, caches, and agent tools. They propose concrete controls without claiming that a checklist establishes legal compliance or a security certification.
Use the schema article to preserve ownership and derivative relationships, then map the lifecycle with the security guide. The agent article adds the question of which tools are exposed and which actions need approval. Test deletion while a job is running and check every related download path. A protected original is not enough when the same information remains readable in a summary or export.
Field guides following
the privacy thread.
Choose between a fixed workflow and model-directed actions, then define tool permissions, approval points, stop rules, and recoverable state.
A practical threat-modeling guide for journal records, generated summaries, exports, background jobs, and administrative access.
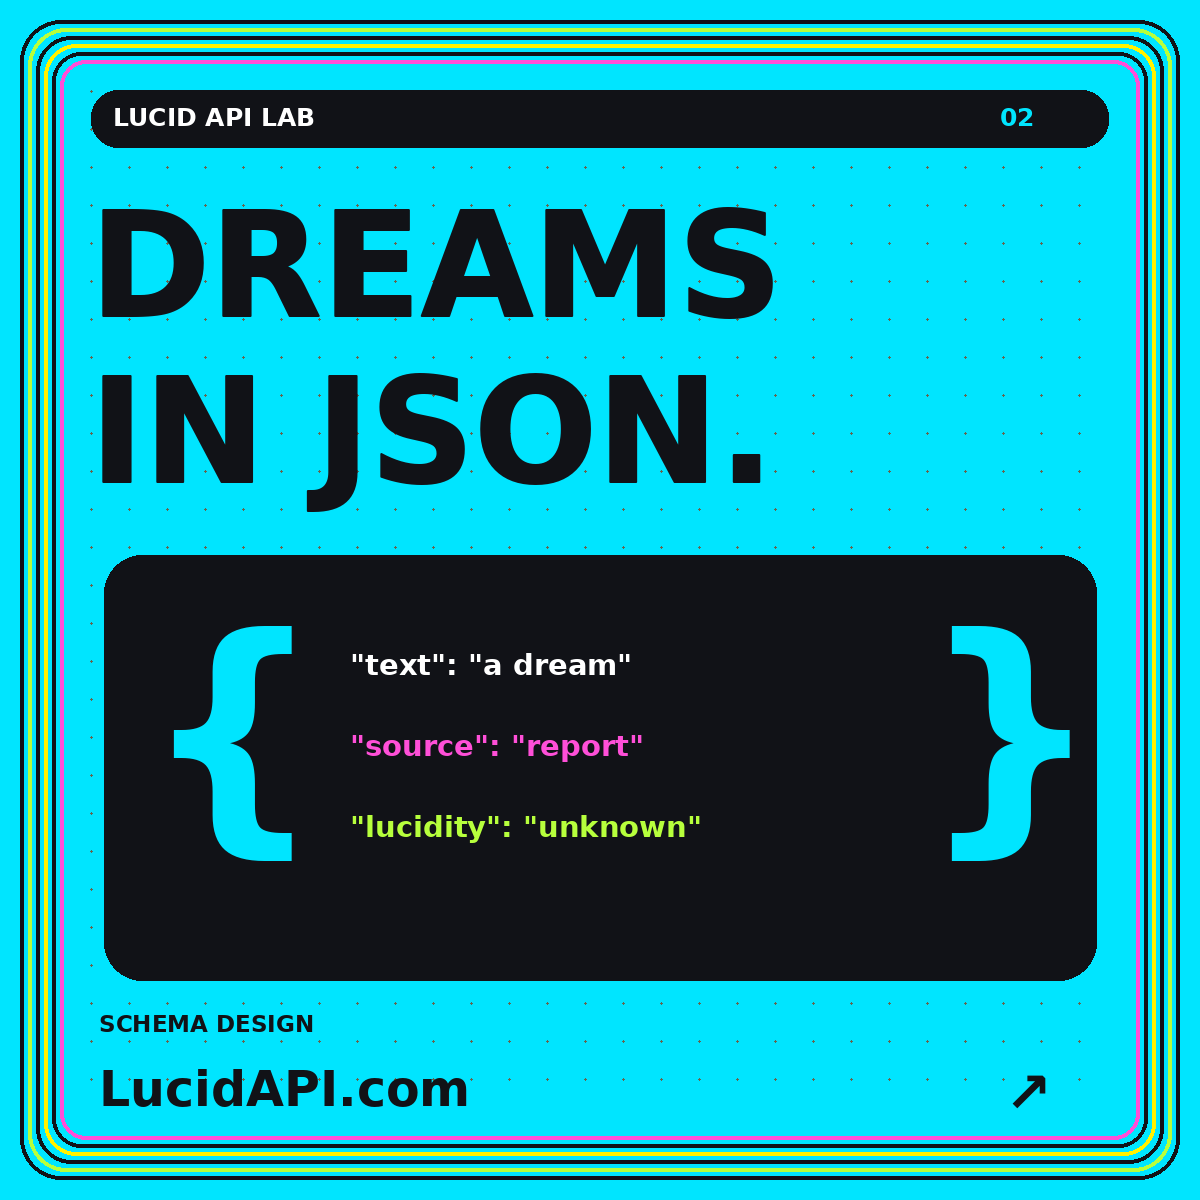
Model dream reports, revisions, consent choices, and generated annotations without turning missing information into false certainty.