A lucid API should make a complicated workflow easier to understand, not hide that workflow behind an impressive name. For a team building around dream journals or AI assistants, the first useful decision is what the interface promises. Does it store a person's account, transform text, or allow software to take an action? Those are different responsibilities, with different failure modes and different permission requirements.
This guide proposes an architecture for your own implementation. It does not describe a hosted LucidAPI.com service. Begin with a narrow outcome: save an authorized journal entry, produce an optional summary, and return a result whose origin remains visible. A small contract that behaves consistently is a more useful starting point than an endpoint promising to understand everything about a dream.
Define the boundary before naming endpoints
Write a sentence describing what each part of the system owns. The journal component owns the user's original account. The transformation component owns generated summaries and extraction results. The workflow component owns the sequence of permitted operations. Keep these responsibilities distinct even when an early prototype runs inside one application.
This boundary makes questions answerable. When a user corrects a journal entry, the original record changes through an explicit revision. A previous summary becomes stale rather than silently becoming the new source. When a model times out, the saved entry remains available. When a workflow is cancelled, cancellation should not remove the user's writing. Design these outcomes before deciding which provider or framework to use.
Describe the contract in a reviewable format
The OpenAPI 3.1 specification describes a language-independent interface for HTTP APIs, including operations, parameters, request bodies, and responses. That makes it a useful reference for documenting an implementation before clients depend on it. A contract is not proof that a server behaves correctly; it is a shared description that your tests must check.
For this project, draft a journal-entry resource, a transformation-job resource, and a result resource. Describe who may create, read, revise, and delete each one. For every successful response, write at least one corresponding failure response. A reviewer should understand missing permissions, invalid input, and unavailable processing without reading application internals or guessing from a generic error message.
Keep original and generated data separate
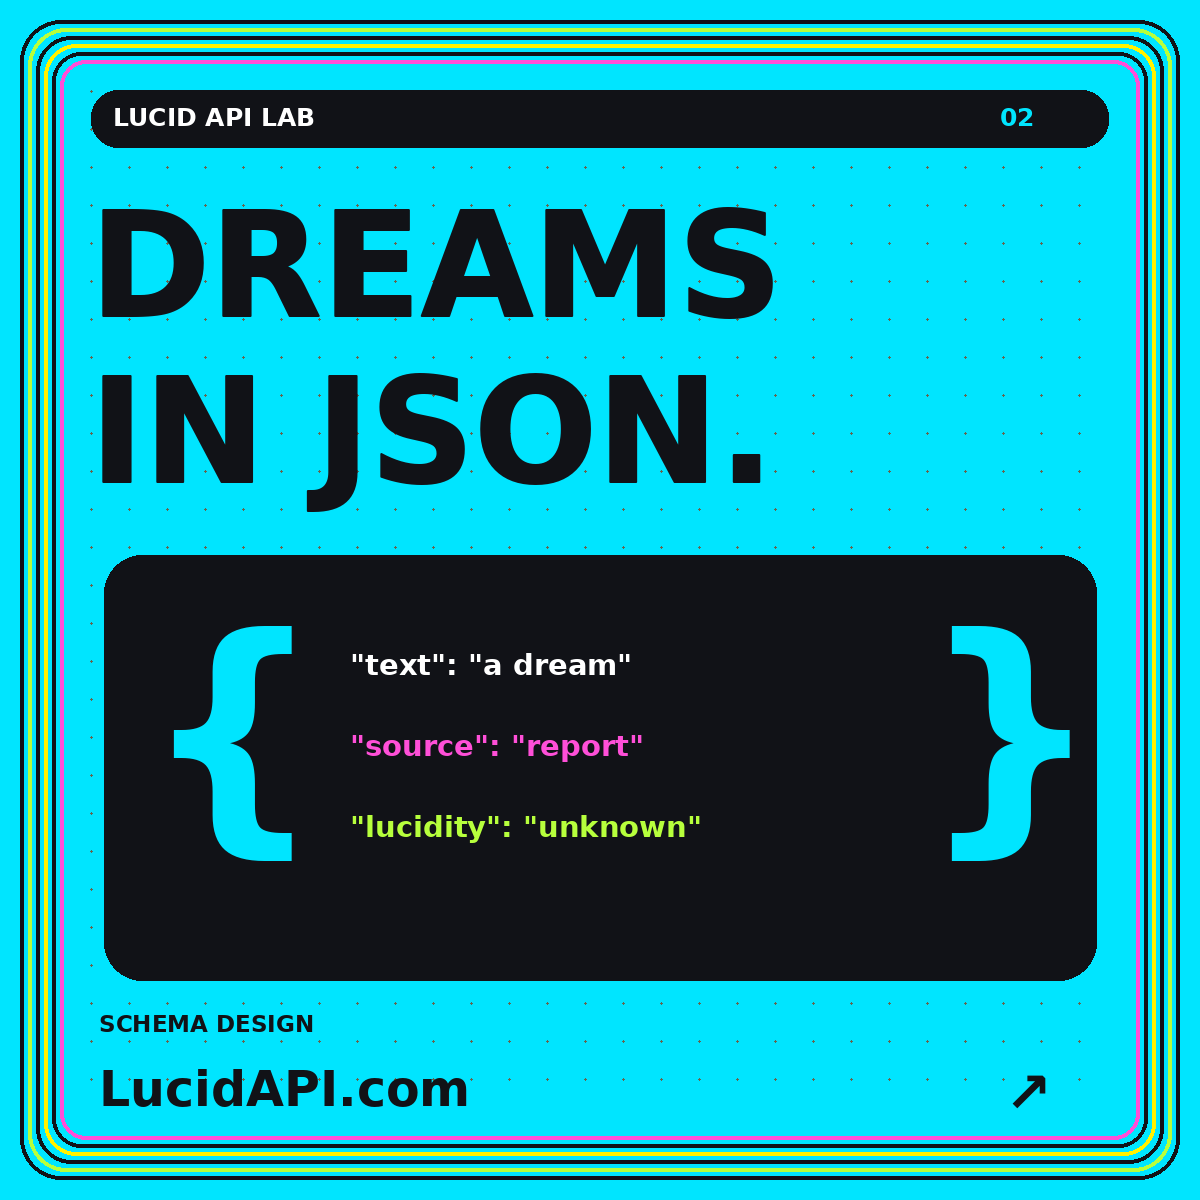
Suppose someone records, “I was on a train, but I cannot remember where it was going.” A summary might describe uncertain travel imagery. It must not replace the original with a confident destination. Give original text and generated text different fields, different provenance, and different editing rules.
A minimal source record
An illustrative record might look like this:
{
  "entry_id": "entry_example_001",
  "revision": 1,
  "text": "I was on a train; the destination is unclear.",
  "source": "user_report",
  "lucidity": "unspecified"
}
The identifier is synthetic and the fields are proposed, not an existing platform contract. Add only what a real use case requires. A user's subjective account does not become a sensor observation because it has been serialized as JSON.
Choose synchronous and asynchronous work deliberately
A short validation operation can return immediately. A transformation that may take longer can return an accepted job identifier, with a separate way to retrieve its state. Consider the experience of a person who closes the application, loses connectivity, or returns after processing has finished. A job record gives that work a name independent of the current screen.
Define understandable states such as queued, running, completed, failed, and cancelled. Treat completed and failed as terminal for a particular attempt. A retry can create a new attempt associated with the same logical job. Avoid a mysterious processing state that never expires. Give clients enough information to stop waiting and explain what remains available.
Make failure part of the interface
A helpful error tells the client which operation failed and whether recovery is possible. Separate invalid content from an expired session, insufficient permission, an exceeded limit, and temporary provider unavailability. Use stable machine-readable error codes alongside a readable explanation. Do not expose sensitive journal text in an error merely to make debugging easier.
Document whether an operation can safely be repeated. For example, submitting the same transformation twice could create duplicate work unless the application implements deduplication. A timeout does not establish that nothing happened. The client needs a way to inspect the job or repeat a request under a defined policy, rather than blindly creating another transformation and hoping for the best.
Put authorization beside the resource
A valid login or token is only the beginning of an access decision. The implementation must also check whether that caller may access this specific entry, job, or result. Keep the ownership relationship visible in the application design. Avoid accepting a user identifier from the request body as sufficient proof of ownership.
Separate ordinary reading from administrative support access. If a future support workflow needs temporary access, make that an explicit capability with a reason and an audit record. Generated summaries deserve the same care as originals when they reveal the same personal information. The dream-data design guide develops these relationships in more detail without assuming a particular database or identity provider.
Design a version policy early
A version policy is a promise about change. Distinguish adding optional information from renaming a field, changing its meaning, or making a previously optional value mandatory. Consider a client that cannot be updated immediately. That client should receive predictable behavior rather than a surprise hidden behind an unchanged endpoint name.
Record the contract version separately from the model identifier and the prompt version. A new model might preserve the HTTP contract while changing output quality. A new contract might reorganize response fields without changing the model. Keeping those identities separate makes rollback and comparison understandable. Publish examples for supported versions and decide how clients learn about deprecations before the first incompatible release.
Build one complete vertical slice
Start with a synthetic entry, an authorized save, a queued transformation, a validated result, and an explicit deletion. Exercise that path through the same boundaries intended for production. Do not begin by implementing every possible dream label, agent tool, and analytics screen. A narrow slice reveals gaps between components while changes are still inexpensive to make.
For the first slice, include an intentionally invalid request and a caller who does not own the entry. Verify that neither reaches model processing. Then simulate a timeout after the provider accepted work. Observe whether the client can recover without creating an uncontrolled stream of duplicate jobs. These tests reveal more about the interface than a polished success-only demonstration.
Decide what the interface will not claim
An API can store reports, organize text, and coordinate software. Those capabilities do not establish that it can read dreams, verify a person's internal experience, or produce a clinically meaningful interpretation. Put narrow descriptions beside each feature. A summary is a summary; a user-reported lucid state remains user-reported.
Also distinguish architecture examples from commercial availability. Without deployed infrastructure, authentication, operational ownership, and actual service terms, a documented route is not a working product. Keep exploration links educational rather than presenting fake access buttons. Teams evaluating an implementation should be able to identify the operator, supported operations, and limitations without interpreting marketing language as a technical contract.
Conclusion: make the next decision easier
The most useful lucid API architecture preserves meaning across boundaries. It separates records from transformations, makes authorization specific, names failure states, and provides a version policy that a client can follow. None of those decisions requires choosing the most elaborate model first.
Take the contract to a frontend developer, a backend developer, and someone responsible for reviewing user-facing language. Ask each person to explain what happens after a failed transformation and after a corrected entry. Differences in their answers identify the next design task. Continue with the Lucid AI API integration overview when the boundaries are clear, and use the reliability guide to turn those promises into testable behavior.